Control and protection of DNS traffic
DNS Patrol is software that protects against threats using Threat Intelligence CZ.NIC from data analysts of the ADAM team and the CSIRT.CZ security team. Suitable for organizations, public administration authorities, medium and large companies.
DNS Patrol protects you
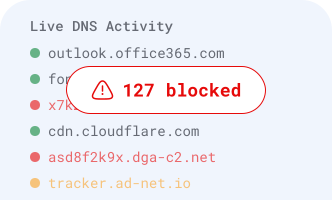
Monitors and analyzes DNS traffic in real-time and helps block malicious domains. DNS Patrol focuses on detecting phishing, malware, and other risks at the DNS level.
Phishing
Blocks domains impersonating legitimate services to steal credentials.
DNS Tunneling
Detects data exfiltration hidden within DNS query traffic.
DGA Detection
Uses machine learning to identify algorithmically generated domains used by malware.
Malware Domains
Blocks connections to known malware distribution and C2 infrastructure.
How DNS Patrol works
Every request is automatically evaluated against known threats and your organization's policies. Safe traffic continues without restriction, while risky or unwanted sites can be blocked automatically.
DNS Query Received
A device on your network makes a DNS request. The query is intercepted by DNS Patrol's recursive resolver.
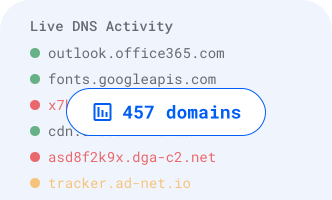
Analyzed & Classified
The domain is checked against Threat Intelligence databases developed and continuously updated by us, as well as customer-defined lists. At the same time, it is analyzed for the presence of DGA domains and DNS tunneling.
Resolved or Blocked
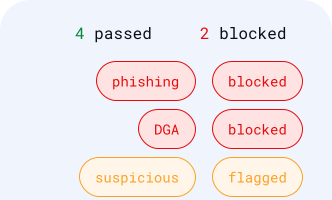
Safe queries resolve normally. Malicious domains are blocked instantly. Suspicious queries are flagged and logged.
Key features of DNS Patrol
DNS Patrol is a solution that protects organizations against security threats related to DNS (Domain Name System) traffic. The system enables secure domain resolution, DNS traffic monitoring, and detection of potential attacks.
Transparent. Community-driven.
DNS Patrol is fully open source under the GNU GPLv3 license. Every component — resolver, admin portal, and client agents — is available for review, audit, and contribution.
Transparent Code
Active community with regular updates and security patches.
Audit Capability
Full audit log — verify security with full access to sources.
Custom Modifications
Custom blocklists and allowlists tailored to your organization.
Active Development
In-house development of Threat Intelligence databases and real-time detection.
Provided Technical Support
CZ.NIC provides Level 3 (L3) technical support
Infrastructure Support
Ensuring the setup and operation of the DNS Patrol system.
Technical Maintenance
Resolving potential issues and handling incidents related to software and infrastructure.
Custom Development
Implementing new features according to specific customer requirements.